Field Guides / Cloud Security Engineer Career Path
Field Guide · Intermediate · 12-15 hours with labsCloud Security Engineer: Securing AWS from Day One
Secure AWS from day one: identity, guardrails, logging, data protection, IaC scanning and incident response, with 15 hands-on labs.
100
pages
pages
15
hands-on labs
hands-on labs
26
interview Q&As
interview Q&As
13
chapters
chapters
This is for you if
- You're a DevOps, SRE or platform engineer pulled into security work
- You know the AWS CLI and some Terraform and want real security depth
- You're aiming for cloud security engineer roles in Canada or the US
- You're preparing for the AWS Certified Security - Specialty (SCS-C03)
What's inside
- IAM policy evaluation explained, plus Access Analyzer checks you can run in CI
- Safe delegation with permissions boundaries, proven with the policy simulator
- Keyless GitHub Actions deploys with OIDC and a correctly scoped trust policy
- SCPs, RCPs, declarative policies, centralized root access and Control Tower 4.0
- A tamper-resistant CloudTrail trail, GuardDuty, and the new Security Hub vs CSPM
- KMS, private TLS-only S3, Macie and Secrets Manager done properly
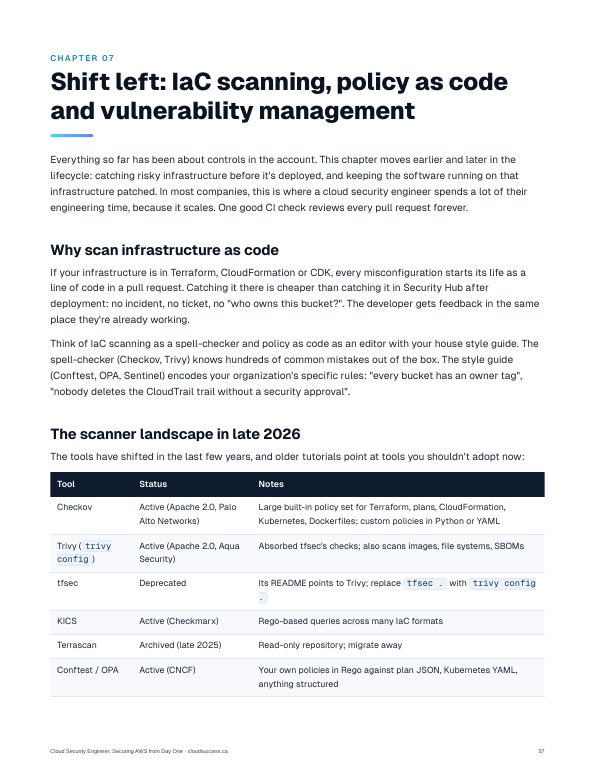
- Checkov, Trivy and Conftest gates for Terraform, plus image scanning and SBOMs
- EventBridge alerts on risky changes and a compromised-key response drill
- SOC 2, ISO 27001 and PCI DSS mapped to real AWS controls, plus 26 interview Q&As
After this guide you can
- Design a multi-account AWS baseline with guardrails that teams can live with
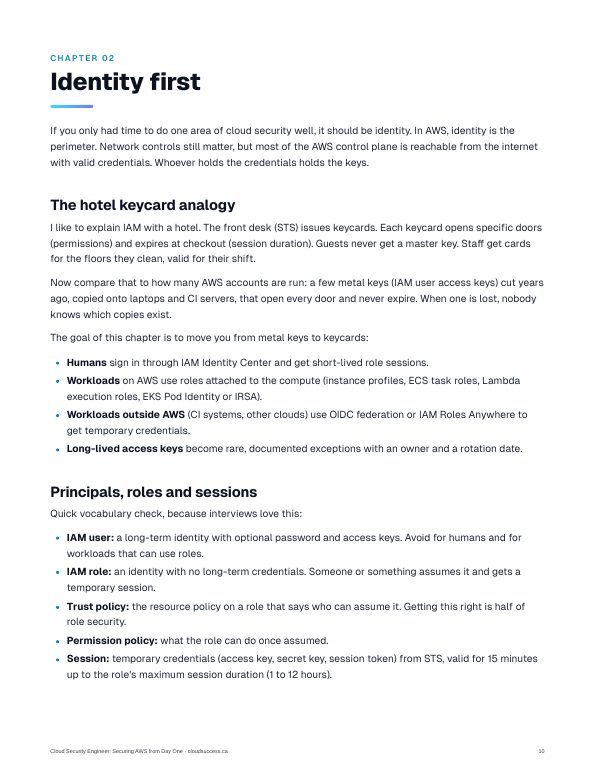
- Replace long-lived keys with Identity Center and OIDC federation
- Make logs tamper-resistant and turn findings into alerts with runbooks
- Block risky infrastructure changes in CI with scanning and policy as code
- Run a calm cloud incident response: contain, preserve, rotate, recover
- Answer senior-level cloud security interview questions with confidence
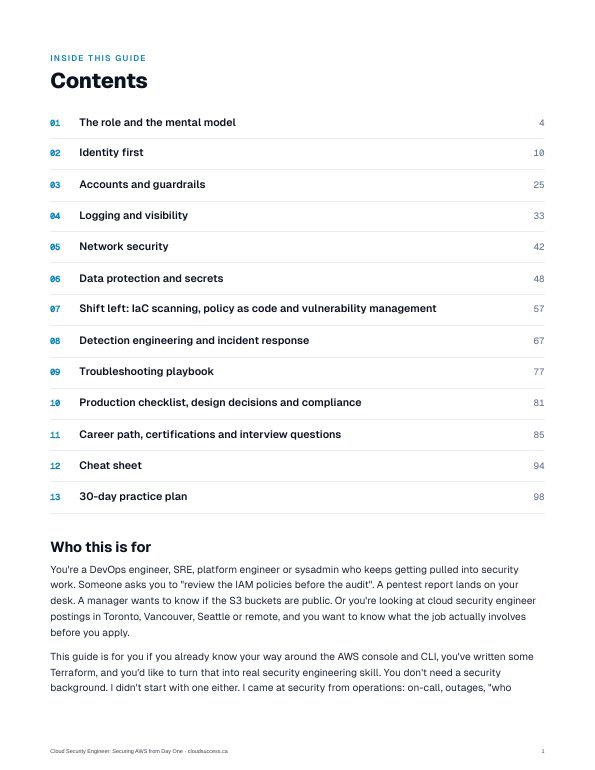
Contents
- The role and the mental modelp. 4
- Identity firstp. 10
- Accounts and guardrailsp. 25
- Logging and visibilityp. 33
- Network securityp. 42
- Data protection and secretsp. 48
- Shift left: IaC scanning, policy as code and vulnerability managementp. 57
- Detection engineering and incident responsep. 67
- Troubleshooting playbookp. 77
- Production checklist, design decisions and compliancep. 81
- Career path, certifications and interview questionsp. 85
- Cheat sheetp. 94
- 30-day practice planp. 98
Written by Randy, a Senior Platform Engineer & SRE who runs production platforms on AWS, GCP and Azure. Companion to the Techworld with Randy episode Cloud Security Engineer Career Path.