Field Guides / Secure CI/CD with GitHub Actions
Field Guide · Intermediate to Advanced · 10-12 hours with labsSecure CI/CD with GitHub Actions
Build fast, locked-down GitHub Actions pipelines with OIDC, least-privilege tokens, signed images, ARC runners and GitOps.
83
pages
pages
12
hands-on labs
hands-on labs
26
interview Q&As
interview Q&As
13
chapters
chapters
This is for you if
- You maintain GitHub Actions workflows and suspect they hold more power and secrets than they should
- You still have long-lived cloud keys in CI and want a safe, keyless path to AWS, GCP or Azure
- You own a platform and need shared workflows, self-hosted runners and a clean handoff to Argo CD
- You're preparing for DevOps, SRE or platform interviews where CI/CD security comes up
What's inside
- A clear mental model of events, runners, tokens and trust boundaries, plus the real attacks that target them
- Production-ready workflow patterns: permissions, concurrency, timeouts, outputs and pinned runner images
- Caching, matrix builds, monorepo path filters with a gate check, and a step-by-step method for speeding up pipelines
- Reusable workflows and composite actions, including permission and secret flow and the trusted-workflow pattern
- Keyless OIDC to AWS, GCP and Azure, updated for the 2026 immutable subject claim format
- Supply chain hardening: SHA pinning, Dependabot cooldowns, zizmor audits, image scanning, artifact attestations and cosign
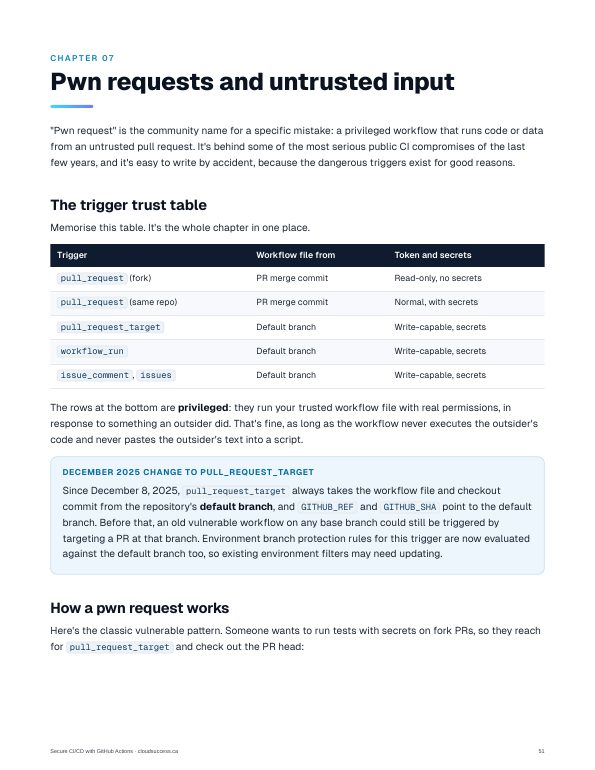
- Pwn requests and script injection explained with a live lab, plus safe patterns for privileged automation
- Environments, approvals and a GitOps handoff to Argo CD by image digest using a GitHub App token
- ARC runner scale sets on Kubernetes, a troubleshooting playbook, checklists, 26 interview Q&As and a 30-day plan
After this guide you can
- Write and review workflows with least-privilege tokens, pinned actions and no injection risks
- Replace stored cloud keys with OIDC trust policies tied to repository, environment and workflow
- Build, scan, attest, sign and verify container images, and deploy them by digest
- Choose between push deploys and GitOps and wire a gated handoff to Argo CD
- Run ephemeral, autoscaling self-hosted runners with ARC and debug them when jobs stall
- Answer senior-level interview questions on CI/CD security with confidence
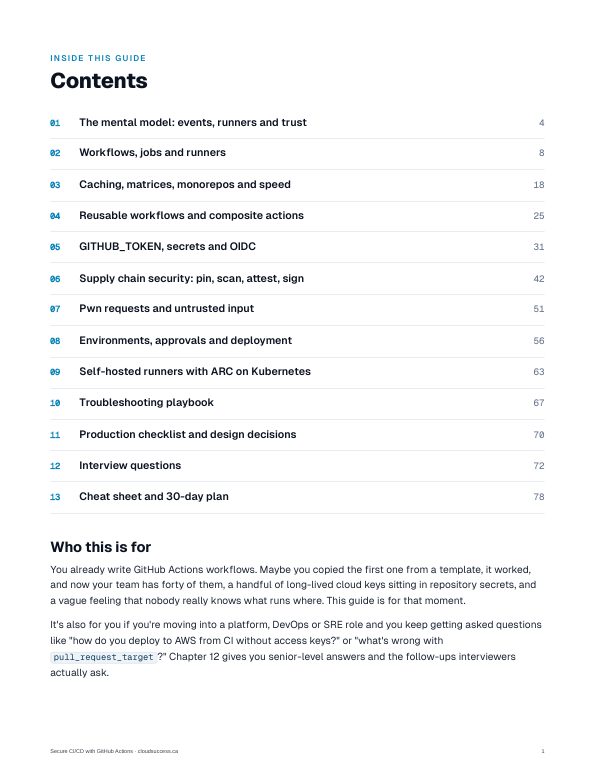
Contents
- The mental model: events, runners and trustp. 4
- Workflows, jobs and runnersp. 8
- Caching, matrices, monorepos and speedp. 18
- Reusable workflows and composite actionsp. 25
- GITHUB_TOKEN, secrets and OIDCp. 31
- Supply chain security: pin, scan, attest, signp. 42
- Pwn requests and untrusted inputp. 51
- Environments, approvals and deploymentp. 56
- Self-hosted runners with ARC on Kubernetesp. 63
- Troubleshooting playbookp. 67
- Production checklist and design decisionsp. 70
- Interview questionsp. 72
- Cheat sheet and 30-day planp. 78
Written by Randy, a Senior Platform Engineer & SRE who runs production platforms on AWS, GCP and Azure. Companion to the Techworld with Randy episode Secure CI/CD with GitHub Actions.