Field Guides / Kubernetes Security Hardening
Field Guide · Intermediate to Advanced · 12-14 hours with labsKubernetes Security Hardening
Harden a real cluster layer by layer: RBAC, Pod Security, NetworkPolicy, secrets, admission, supply chain, audit and response.
90
pages
pages
16
hands-on labs
hands-on labs
20
interview Q&As
interview Q&As
13
chapters
chapters
This is for you if
- You run Kubernetes and someone has asked you to prove the cluster is secure
- You know Deployments, Services and RBAC basics but not how attackers move through a cluster
- You're preparing for the CKS exam or a platform, SRE or security-focused interview
- You need a rollout order that hardens production without breaking every deploy
What's inside
- The attack path every cluster compromise follows, mapped to the control that breaks each step
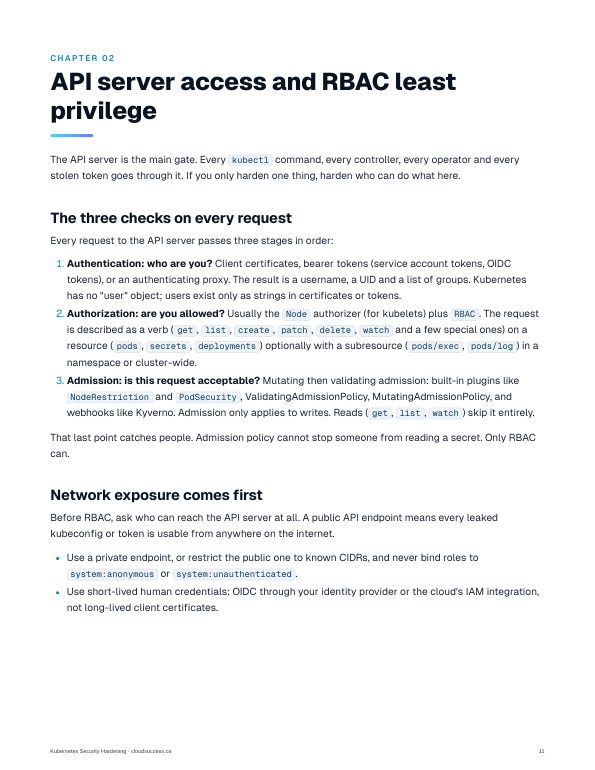
- RBAC audits that find wildcard roles, cluster-admin sprawl and the quiet create-pods escalation
- Pod Security Admission rolled out from warn to enforce, plus hardened securityContext and seccomp
- Default-deny NetworkPolicy with DNS, egress and metadata-endpoint rules that actually hold
- Encryption at rest proven in etcd, key rotation, and External Secrets Operator
- ValidatingAdmissionPolicy in CEL and Kyverno 1.19 CEL policies with background reports
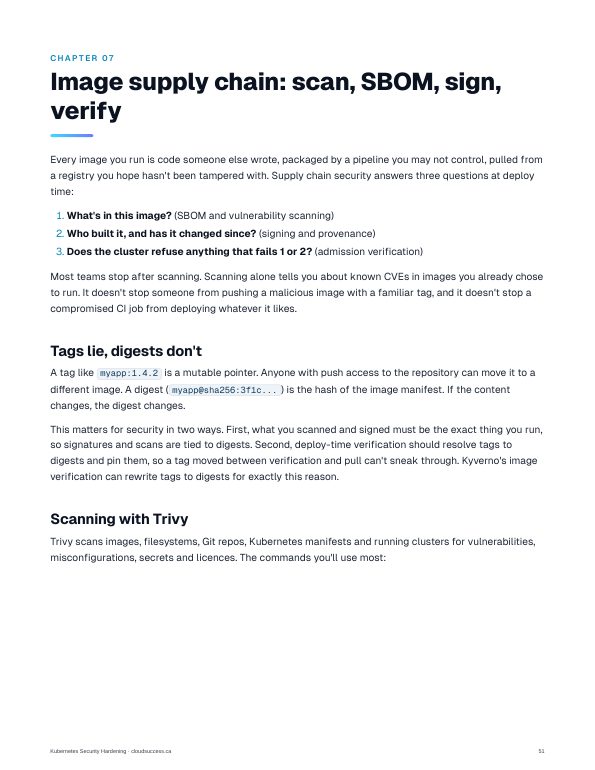
- Trivy scanning, SBOMs, cosign v3 signing and admission-time signature verification
- Audit log queries for RBAC changes, secret reads and exec, plus Falco routed to Slack and Prometheus
- kube-bench node checks, a compromised-pod response runbook and 20 interview questions
After this guide you can
- Audit RBAC and service accounts and remove the escalation paths you find
- Enforce restricted Pod Security and default-deny networking without breaking apps
- Protect secrets at rest and in the supply chain, and block unsigned images at admission
- Turn audit logs and runtime detection into alerts people actually act on
- Contain a compromised pod, preserve evidence, rotate credentials and rebuild with confidence
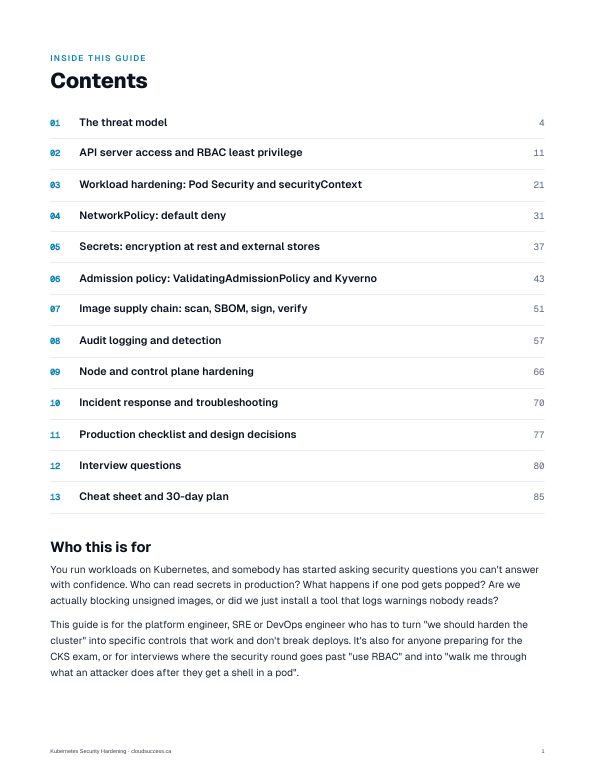
Contents
- The threat modelp. 4
- API server access and RBAC least privilegep. 11
- Workload hardening: Pod Security and securityContextp. 21
- NetworkPolicy: default denyp. 31
- Secrets: encryption at rest and external storesp. 37
- Admission policy: ValidatingAdmissionPolicy and Kyvernop. 43
- Image supply chain: scan, SBOM, sign, verifyp. 51
- Audit logging and detectionp. 57
- Node and control plane hardeningp. 66
- Incident response and troubleshootingp. 70
- Production checklist and design decisionsp. 77
- Interview questionsp. 80
- Cheat sheet and 30-day planp. 85
Written by Randy, a Senior Platform Engineer & SRE who runs production platforms on AWS, GCP and Azure. Companion to the Techworld with Randy episode Kubernetes Security Hardening.